Smarter technology helps businesses stay ahead of increasingly sophisticated scammers
FOUR in 10 Malaysians surveyed have experienced hacking or data theft, with 18 per cent reporting financial consequences from such incidents.
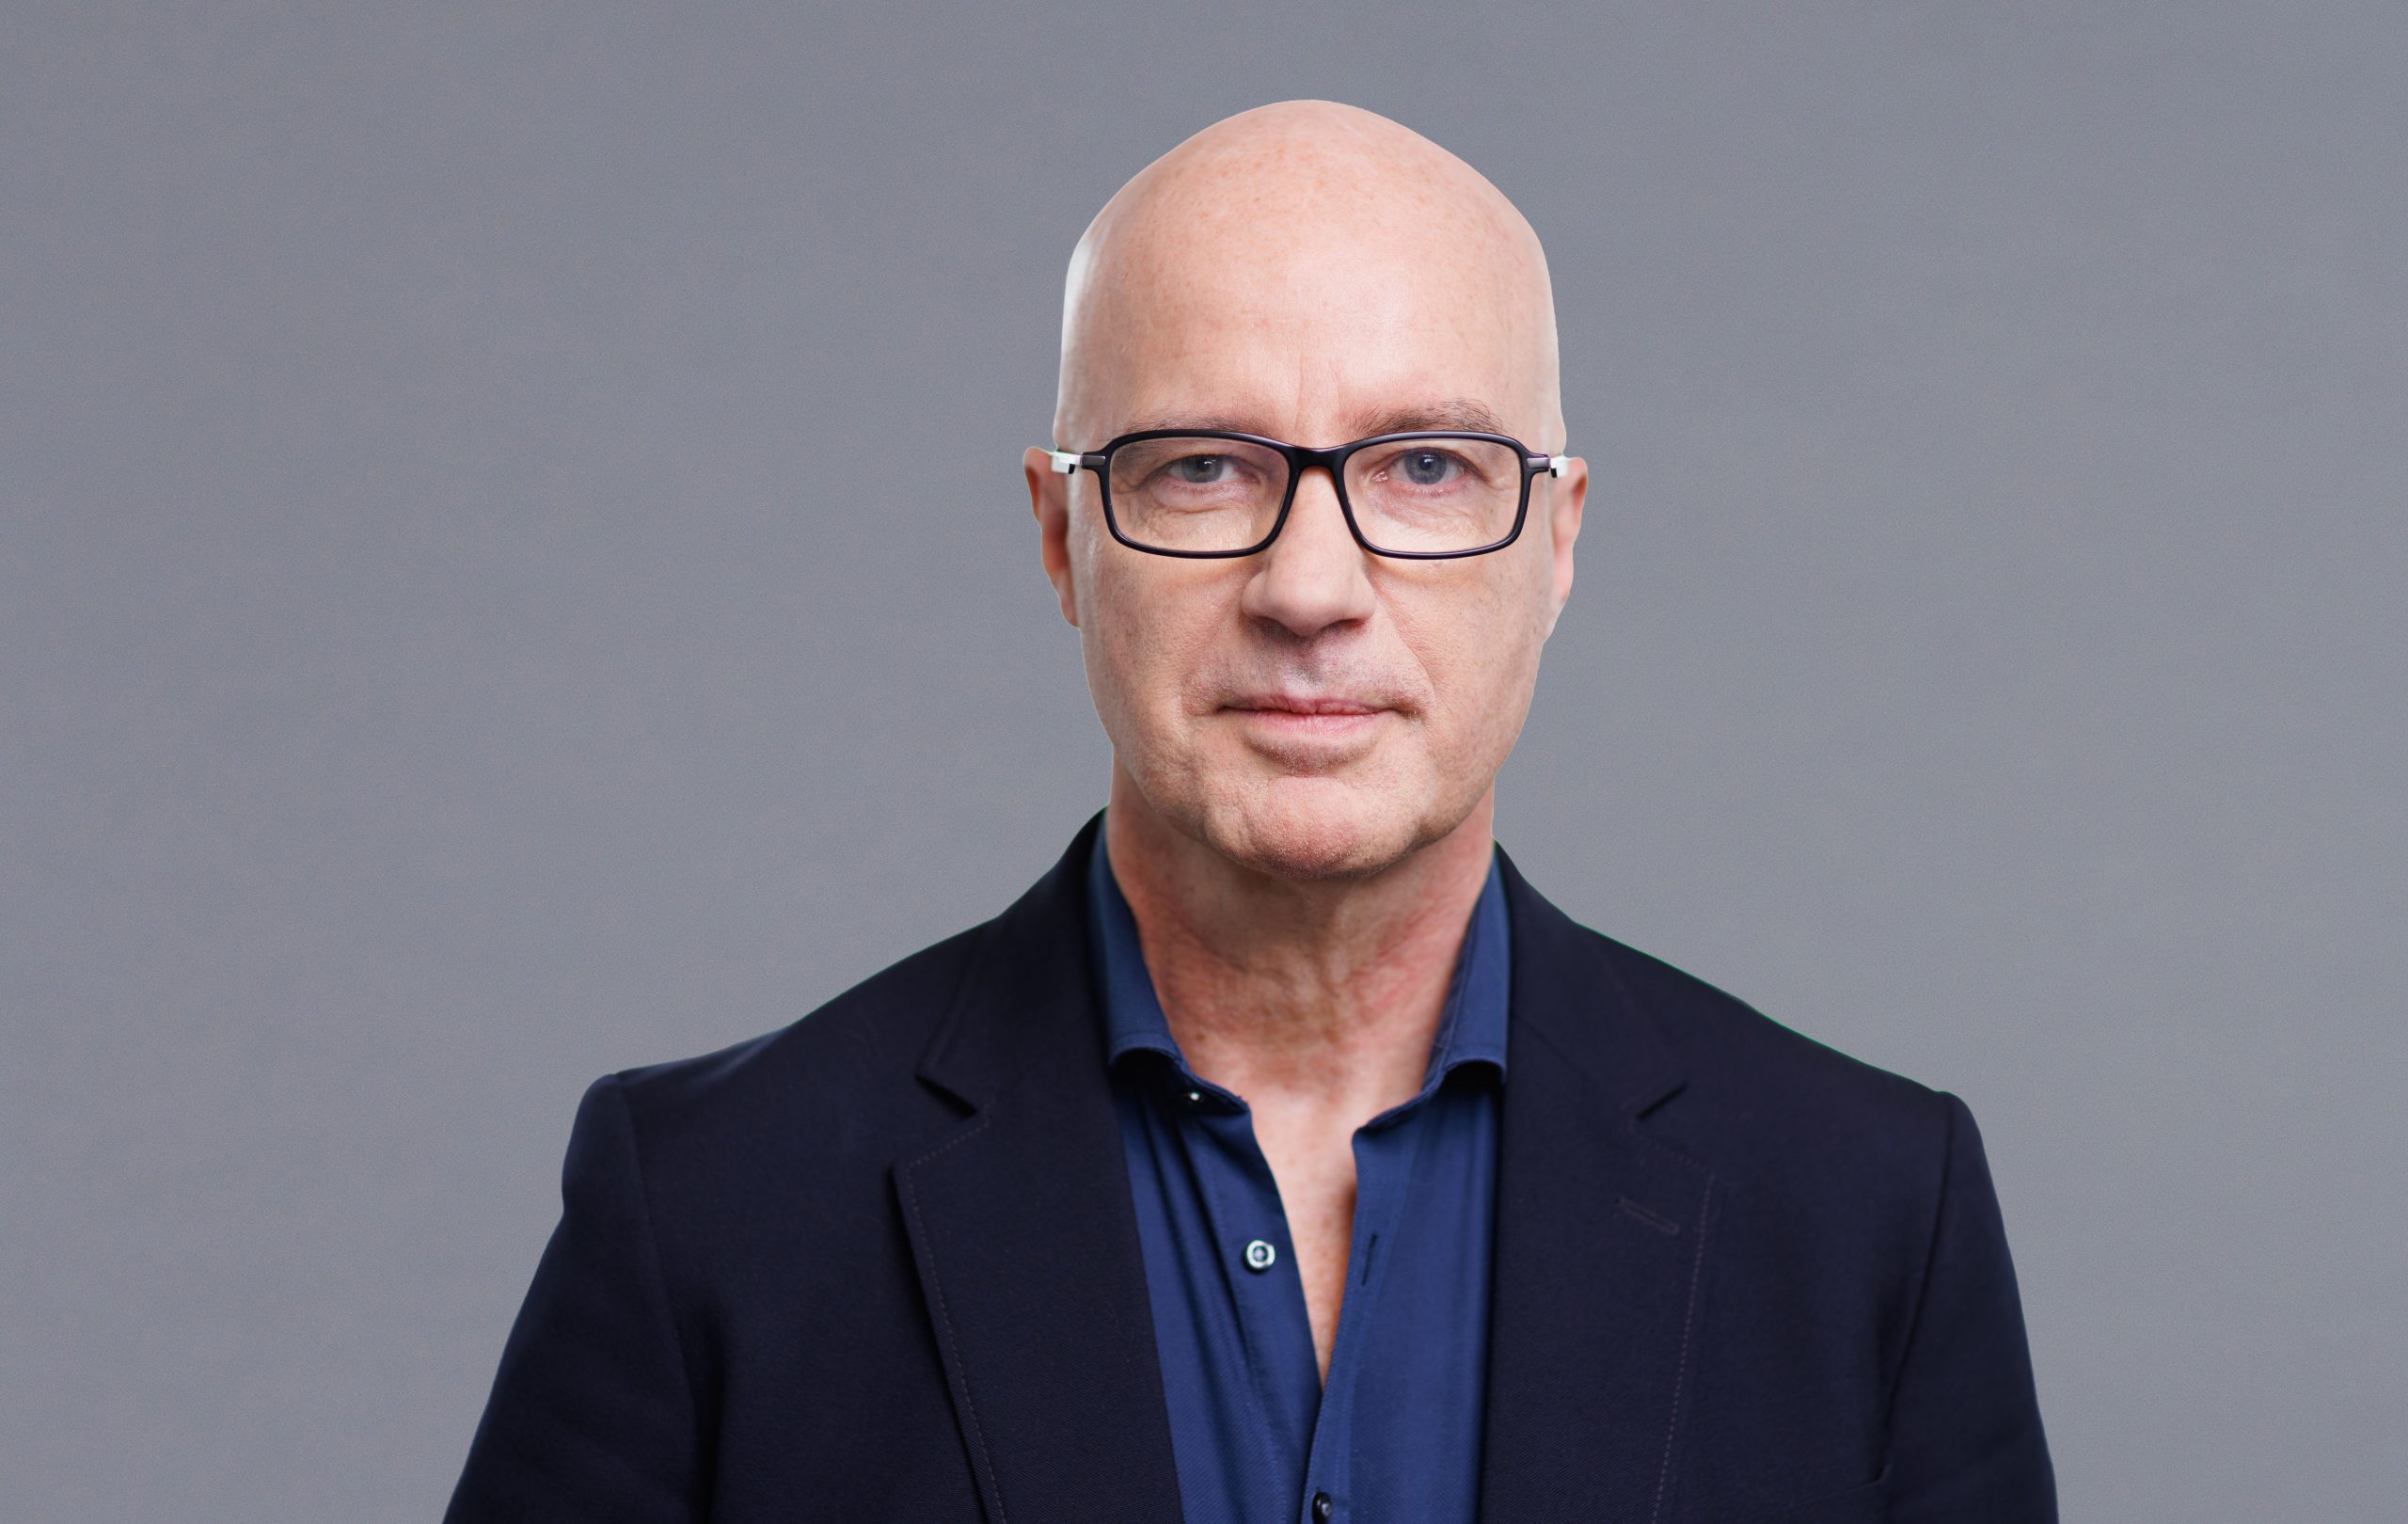
IDEMIA Secure Transactions chief technology officer Marc Bertin said the findings highlighted growing concerns over online security despite 98 per cent of respondents frequently using digital services.
He said 87 per cent were concerned about digital fraud, while 91 per cent feared personal data theft.
More than half, or 53 per cent, felt more vulnerable online than five years ago.
“Although 91 per cent of Malaysian respondents are aware of potential cyber risks, only 42 per cent said they understood them well,” he told Sarawak Tribune.
Bertin said the findings reflected a gap between digital adoption and consumer confidence in online security.
“What this tells us is that digital adoption and digital trust do not necessarily progress at the same pace,” he said.
He said businesses needed to strengthen protection without complicating digital services, as consumers increasingly expected security to be incorporated into everyday transactions.
AI raises sophistication of cyber fraud
Bertin said artificial intelligence (AI) was making cyber fraud more sophisticated, particularly through phishing, impersonation and social engineering.
He said 80 per cent of Malaysian respondents who felt more vulnerable online cited increasingly sophisticated AI-driven attacks and fraud as a reason, compared with 67 per cent globally.
“Generative AI can make phishing messages more convincing, adapt them to different languages and contexts, and make impersonation attempts more realistic through technologies such as voice cloning and deepfakes,” he said.
Across the countries surveyed, increasingly sophisticated AI-driven cyberattacks were the most frequently cited reason among respondents who felt less secure online.
However, Bertin said AI could also help businesses identify suspicious activities and respond more quickly to potential threats.
“But AI is not only a source of risk. It can also help organisations identify unusual patterns and potentially detect suspicious activity more quickly,” he said.
He stressed that AI should complement existing cybersecurity systems, supported by appropriate governance and human oversight.
Cybersecurity must begin at design stage
Bertin said businesses should incorporate cybersecurity measures during the initial development of digital services rather than adding protection after systems were completed.
He said 55 per cent of Malaysian respondents identified personal data protection as among the most important security features of digital services.
“Secure by design means considering security at the same time as the service itself is being designed, rather than treating it as an additional layer at the end of the development process,” he said.
He said customer authentication, personal data protection and sensitive financial information should be addressed from the outset.
In digital payments, he cited tokenisation as an example of protecting sensitive information without complicating transactions.
He explained that tokenisation replaced sensitive payment credentials with tokens, reducing the value of information exposed during a security breach.
Bertin said incorporating security early also made future system upgrades and technology integration easier.
“Adding it later can make integration and future upgrades more complex, while designing it from the beginning makes it easier to balance security, simplicity and scalability,” he said.
SMEs face different security challenges
Bertin said small and medium enterprises (SMEs) and larger organisations faced different cybersecurity challenges because of differences in resources, expertise and existing systems.
He said SMEs often lacked specialist knowledge and financial resources to develop sophisticated security capabilities independently.
Smaller businesses should therefore consider platforms and services with established protection measures.
Larger organisations, meanwhile, generally had more resources but faced difficulties maintaining consistent security across multiple systems, technologies and business partners.
He said businesses of all sizes needed adaptable security systems to respond to technological changes and emerging threats.
“What both have in common is the need to plan for change. Technologies and threats evolve, so security architectures need to be adaptable as well,” he said.
Stronger security without complicated transactions
Bertin said businesses could strengthen online security without requiring customers to undergo identical verification procedures for every transaction.
He said authentication requirements should reflect the level of risk, allowing routine transactions to proceed with fewer interruptions while introducing additional checks when necessary.
“A customer using a recognised device and behaving in a familiar way may not need the same level of verification as someone connecting from an unfamiliar device or attempting an unusual transaction,” he said.
He cited FIDO-based authentication as technology that could strengthen security while simplifying customer verification.
FIDO standards reduce reliance on passwords through phishing-resistant authentication methods, including biometrics, security keys and personal identification numbers (PINs).
Bertin said IDEMIA Secure Transactions had developed FIDO-based solutions allowing payment cards to function as secure authentication devices.
“The technology allows customers to tap their payment cards to log in to digital services or approve sensitive operations,” he said.
The company had also developed a secure FIDO server supporting passwordless authentication for banking and e-commerce services.
He said businesses should explain additional verification requirements clearly so customers understood why security checks were necessary.
“Much of the security can operate in the background, but when users are asked to take an additional step, they should understand why it is happening and what they need to do,” he said.
Businesses urged to prepare for quantum threats
Bertin said businesses should begin assessing cybersecurity risks associated with quantum computing, particularly where sensitive information required long-term protection.
He said 83 per cent of Malaysian respondents familiar with quantum computing regarded it as a potential threat to digital security, although understanding of the technology remained limited.
One concern involved the possibility that encrypted information collected today could be decrypted in the future using advanced quantum computers.
“Encrypted information collected today could potentially be decrypted in the future as quantum capabilities develop,” he said.
Known as the ‘harvest now, decrypt later’ scenario, the threat was particularly relevant to organisations holding sensitive information requiring protection for many years.
Bertin said businesses should identify where cryptography was used and determine which systems would be most difficult to upgrade.
They should also develop crypto-agility, allowing cryptographic algorithms to be updated as security standards evolved without redesigning entire systems.
He stressed that businesses did not need to replace existing cryptographic systems immediately, as migration towards post-quantum protection would be gradual.
Bertin said IDEMIA Secure Transactions had been developing post-quantum security technologies across financial services, mobile connectivity, the Internet of Things (IoT) and critical infrastructure.
He said Juniper Research ranked the company first in its 2026 Post-Quantum Cryptography Competitor Leaderboard, assessing 19 global vendors on capability, capacity, product strength and strategic vision.
The ranking reflected its approach to post-quantum security, covering software, advanced hardware components and solutions designed for future cryptographic standards.
“The priority today is to understand the exposure, establish a roadmap and begin testing the technologies required for the transition, particularly for systems and data that need to remain protected for many years,” he said.